GitHub Pays $100,000 Bounty for Critical RCE Flaw in Git Push Pipeline
3 min read
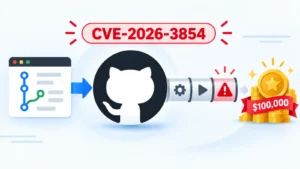
GitHub has awarded security researcher Saif Ghani a $100,000 bug bounty after the disclosure of CVE-2026-3854, a critical remote code execution vulnerability affecting GitHub’s Git push processing pipeline.
The reward is reportedly the largest publicly disclosed payment made through GitHub’s Vulnerability Reward Program. Ghani, known on X as @sagitz_, announced the bounty on July 22, 2026.
GitHub Security later publicly acknowledged the researcher, confirming it addressed the issue through coordinated disclosure and remediation.
The vulnerability reportedly enabled an unauthenticated attacker to execute arbitrary commands on GitHub backend infrastructure by submitting a specially crafted repository URL during Git-related operations.
The flaw stemmed from how a vulnerable service processed repository data and URLs in the Git push workflow. Remote code execution vulnerabilities are among the most serious flaws affecting software platforms because they can allow attackers to run commands within a targeted environment.
GitHub Pays Bounty for Git Push RCE Flaw
In this case, successful exploitation could have provided access to an affected server context, creating risks for repository integrity, source code confidentiality, credentials, and software supply-chain security.
According to the disclosed technical details, the attack path involved malicious repository input that reached backend processing components without proper sanitization or safe handling.
An attacker could allegedly use crafted values to manipulate command execution behavior and obtain shell-level access to the vulnerable environment.
Once code execution is achieved on a source code hosting platform, the impact can extend beyond a single repository. A threat actor could potentially access repository secrets, modify build-related files, alter source code, or interfere with Git objects handled by the service.
Such access could support downstream supply-chain attacks by inserting malicious code into projects trusted by developers and enterprises.
GitHub reportedly deployed mitigations shortly after receiving the report and completed a patch rollout across affected services.
The coordinated disclosure process allowed the company to fix the issue before detailed exploitation information became widely available.
CVE-2026-3854 highlights the security importance of Git infrastructure, especially repository URL parsing, Git protocol handling, server-side hooks, archive generation, and backend automation.
These components often process attacker-controlled data and may interact with operating system commands, internal APIs, storage systems, and credentialed services.
According to RuntimeWire, GitHub’s $100,000 payout highlights the potential impact of a platform-level vulnerability affecting both public and private repositories.
The company’s Vulnerability Reward Program offers high rewards for critical flaws that could compromise core GitHub services, with top-tier payments reaching up to $150,000.
The incident also demonstrates why bug bounty programs remain important for major developer platforms. External researchers can identify complex attack paths that automated testing and internal reviews may miss, particularly where Git operations, cloud infrastructure, and supply-chain workflows intersect.
For organizations using GitHub, the case reinforces the need to protect repository secrets, enforce signed commits, review CI/CD workflow changes, apply branch protections, and monitor unusual Git activity.
A compromise at a major code-hosting provider can create a wide downstream security impact, making rapid vulnerability reporting and remediation essential for the wider software ecosystem.
Learn 7 Metric-Gated AI SOC Deployment Phases – Download Free AI SOC Deployment Playbook 2026.
The post GitHub Pays $100,000 Bounty for Critical RCE Flaw in Git Push Pipeline appeared first on Cyber Security News.
Kaynak: Cyber Security News
Yayin Tarihi: 14.09.2026 08:50